Keep sensitive video and sensor processing on site.
Use a local edge architecture to minimize data movement, upload only necessary events and maintain clearer separation between device and management networks.
Disable unused services and apply credential, firewall and logging policy.
04
Evidence test
Verify data minimization, access control, update, rollback and audit logs.
05
Support plan
Publish the support period, vulnerability intake and customer notification process.
PoC and acceptance
Evidence to collect before production.
Acceptance criteria should be written into the PoC plan and measured under representative load and failure conditions.
Data inventory
Document raw, derived, retained and exported data.
Secure boot
Show the implemented boot chain and failure behavior, not only a feature claim.
Identity and keys
Unique credentials, protected storage, rotation and recovery.
Update security
Signed package, authorization, rollback and interrupted-update recovery.
Exposure
Port, service, firewall, remote access and dependency review.
Lifecycle
SBOM, vulnerability channel, response process and support end date.
Solution boundary
Local processing can support privacy goals but does not by itself establish GDPR, UK GDPR, sectoral or customer-policy compliance. A project-specific legal and security assessment is still required.
Recommended starting configuration
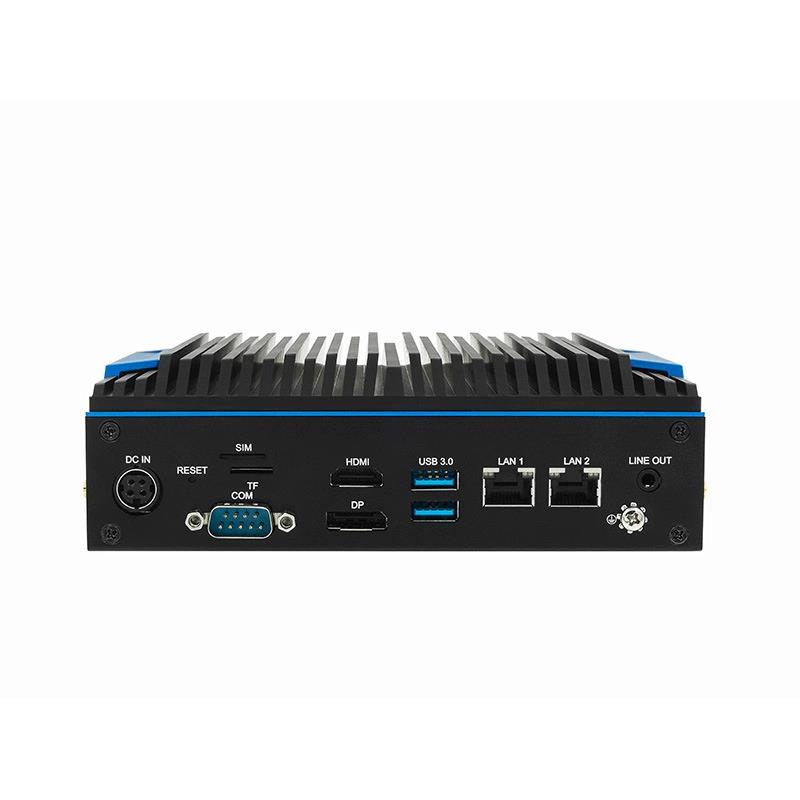
C5-BOX
Finalize the SKU only after the interfaces, workload, environment, software scope and certification route are known.